Security engineering · Texas
Cryptography built for the next threat.
Quantum-resistant. Deadline-respecting.Winternitz is a security engineering practice founded by Kyeson Blake Utley. We migrate systems to post-quantum cryptography, engineer and audit cryptocurrency and custody infrastructure, and break your systems in-house before an attacker does.
$ winternitz --capabilities
post-quantum migration ........ ok
custody engineering ........... ok
smart-contract audits ......... ok
penetration testing ........... ok
fractional CTO ................ ok
excuses ....................... not found
↑ That’s a real Winternitz hash chain, computed live in your browser: a random secret hashed 15 times with SHA-256. Click it to roll a new one. How it works →
What we do
PQC
Post-quantum migration
Inventory your cryptography, rank what a future quantum computer breaks first, and move it to ML-KEM, ML-DSA and hash-based signatures without breaking production.
// before Q-Day, not after
Chain
Crypto & custody engineering
Wallets, signing services, key ceremonies and settlement flows designed around the places funds are actually lost: key handling and trust boundaries.
// “not your keys” applies to attackers too
Audit
Smart-contract & crypto audits
Line-level review of contracts, protocols and cryptographic code, with reproducible proof for every finding and a re-test after you fix.
// immutable bugs are the worst kind
Offense
Penetration testing
Web, API, cloud, network and red-team engagements run entirely in-house. No subcontractors ever touch your environment.
// we knock first, with paperwork
Build
Custom engineering
Security-critical software built from a blank page when nothing off the shelf fits: protocols, services and internal tools.
// no templates were harmed
Helm
Fractional CTO
Senior technical leadership on demand: architecture, security posture and roadmap, without a full-time hire.
// all of the judgment, none of the corner office
By the numbers
Size of a Winternitz signature with SHA-256 and w = 16. Small enough to ship, strong enough to trust.
Hashes from secret key to public key on each chain. That’s the whole trick.
Post-quantum security left in a 256-bit hash after Grover’s algorithm takes its cut.
Subcontractors who will ever touch your environment. Everything is done in-house.
Quantum readiness check
Five honest questions, thirty seconds, no email required. Nothing leaves your browser.
Free tools
Risk
Quantum risk calculator
Is your data already exposed to harvest-now, decrypt-later? Find out in thirty seconds.
Hash
Hash avalanche playground
Change one letter, watch half the bits of a SHA-256 hash flip.
Compare
Signature size chart
Classical vs post-quantum signatures, byte for byte.
Field notes
Harvest now, decrypt later: is your data already exposed?
Why data encrypted today can be read by tomorrow's quantum computers, how to use Mosca's inequality to tell whether you're already late, and what to fix first.
Stateful signatures and the backup that ate your keys
LMS and XMSS are standardized, quantum-safe and fast. They also break catastrophically if a one-time key is used twice. Here's how ordinary operations cause that, and how to prevent it.
What Q-Day means for crypto custody
Bitcoin and Ethereum rely on elliptic-curve signatures that a large quantum computer could break. Which coins are exposed first, why address reuse matters, and what custodians can do now.
Why “Winternitz”
The Winternitz one-time signature is one of the oldest ideas in public-key cryptography and one of the few that a quantum computer doesn’t threaten. It needs nothing but a hash function: hash a secret enough times and you get a public key, and anyone can check a signature by finishing the hashing. Its descendants sit inside today’s standardized post-quantum signatures, XMSS, LMS and SLH-DSA.
That’s the approach we take to engineering: rely on the fewest, best-understood assumptions, and design for the attacker that’s coming, not just the one you have. See how Winternitz signatures work, with a live demo →
How we work
Scope
A discovery call, a written scope and a fixed price. You know exactly what you’re getting before anything starts.
Authorize
Signed authorization and NDA before a single packet is sent or a line of code is read.
Execute
Regular status updates, and critical findings reported the moment we confirm them.
Deliver
A report your board and your engineers can both act on, a live walkthrough, and a re-test of your fixes.
Founder
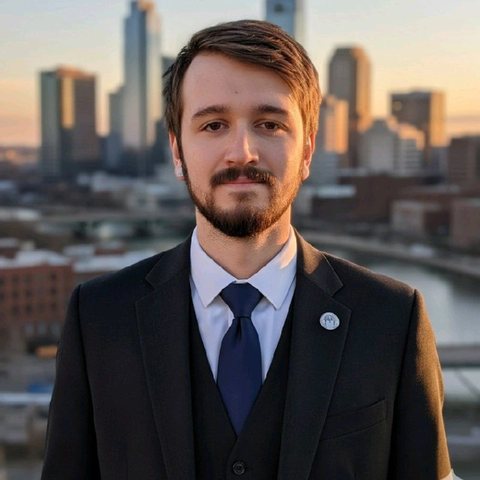
Kyeson Blake Utley is a Texas security engineer. He spent years in blockchain forensics, tracing stolen cryptocurrency for fraud victims at SpookyGood, the firm he founded in 2020, then served as CTO of Justice Solutions Group. Winternitz is where he does that work now.
Have a system that has to hold?
Tell us what you're protecting and when it has to be ready. You'll get a straight answer on scope, timeline and price, usually within one business day.